[ Case study · Governance, risk & compliance ]
Compliance at the speed of the business.
An AI assessment and risk engine for Big 4 advisors and regulated enterprises. It maps controls across DORA, NIS2, ISO 27001, SOC 2, GDPR and CSRD, and turns weeks of spreadsheet work into a framework ready in days.
Control mappingExample
| Control | DORA | NIS2 | SOC 2 | ISO 27001 | GDPR |
|---|---|---|---|---|---|
| Access reviews | |||||
| Incident response | |||||
| Third-party risk | |||||
| Backup and recovery | |||||
| Encryption at rest |
Assessed once, reused in 4 frameworks
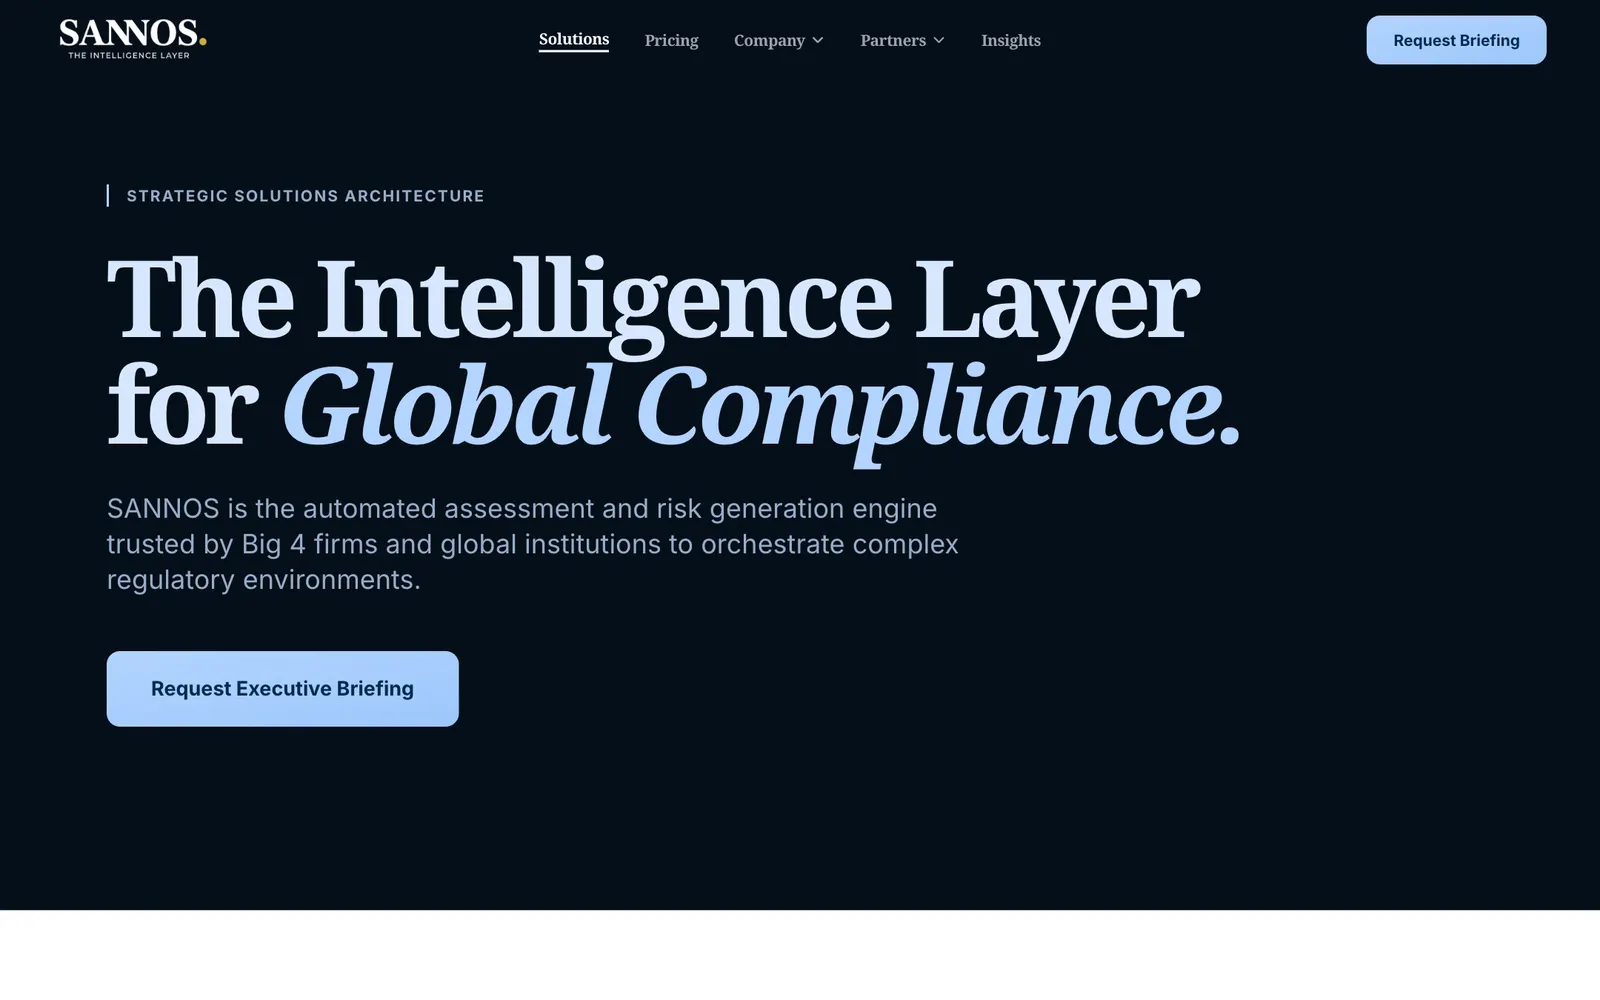
Four Problems to Solve
Founded by Big 4 risk veterans Ralph Bengtsson and Anders Søborg, Sannos serves audit firms and global institutions that juggle overlapping regulations across dozens of entities.
- Sector
- RegTech & GRC
- Users
- Big 4 firms, enterprises
- Frameworks
- DORA, NIS2, SOC 2, CSRD +
- 1-2 daysFramework setupto deploy a new framework, down from several weeks
- 60%Review effortfewer analyst hours per control assessment
- 4xReuseaverage reuse of each piece of evidence across frameworks
- 15+Frameworksregulations and standards mapped in the library
Figures reflect early engagements delivered on the platform by advisory partners.
A living control library with an AI analyst on top
One proprietary control library mapped across more than a dozen frameworks, so evidence collected once counts everywhere it applies.
From regulation to signed-off report
How an engagement moves through the platform.
- 1
Framework selected
Pick DORA, NIS2, SOC 2 or a bespoke set. Proprietary frameworks deploy in one to two days.
- 2
Evidence ingested
Policies, logs and questionnaires uploaded once and linked to every control they satisfy.
- 3
AI drafts the ratings
Each control assessed with cited evidence and a confidence score for the reviewer.
- 4
Risks and reports issued
Gaps turned into owned risks, then exported as partner-ready reports.
Built with
- LLM + RAG Pipeline
- Vector Search
- Node.js
- PostgreSQL
- React
- SSO / SAML
- EU Data Residency
Before
Each engagement began in a fresh spreadsheet, controls were re-assessed for every framework, and audit trails were stitched together at the end.
After
Advisors pick a framework, reuse evidence across regulations, review AI-drafted ratings and export a defensible report in a fraction of the time.
- Cross-framework control library
- AI assessment and risk engine
- Enterprise reporting suite
Planning an AI compliance platform?
You get a clear plan, a fixed price and a team that has shipped this kind of product before.
Keep Exploring
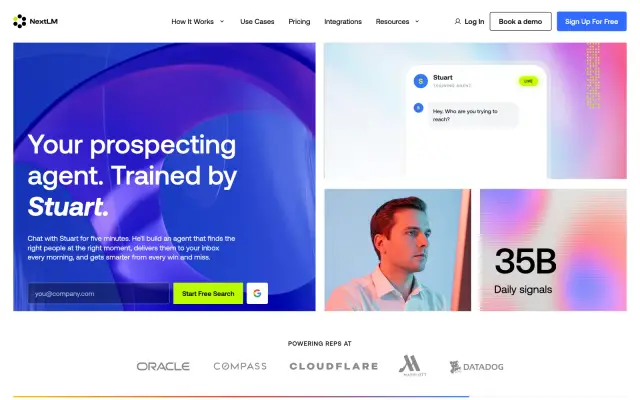
AI · Sales intelligence
NextLM
An AI prospecting agent that turns 35 billion daily intent signals into a ranked list of ready buyers every morning.
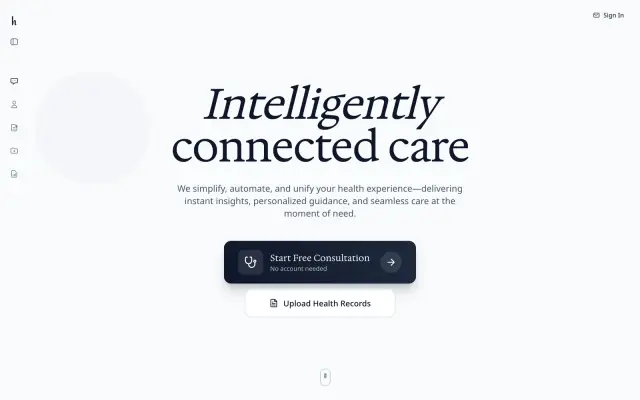
AI · Digital health
Healthzy
An AI health companion that knows your records, reads your reports and gives clear guidance in under two minutes.
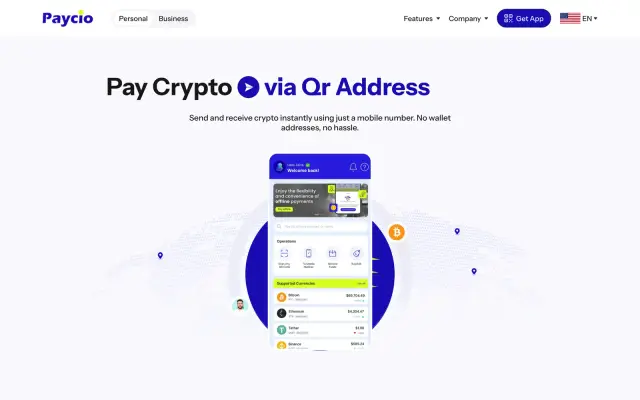
FinTech · Crypto payments
Paycio
A crypto wallet and payment gateway that sends funds to a phone number, works offline and settles across chains.
Let's build your next product together
Book a free strategy call and leave with a clear plan and estimate. No commitment.
- 01Pick a time that suits you
- 0230 minutes on scope, stack, timeline and budget
- 03Fixed-price proposal, NDA on request